A 10-port industrial firewall and router for OT perimeters
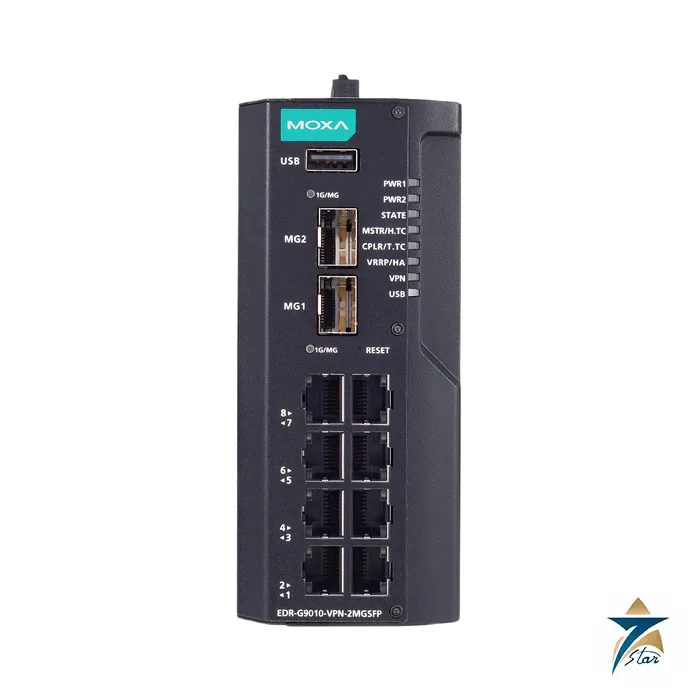
The Moxa EDR-G9010-VPN-2MGSFP combines a firewall, NAT, VPN, router and managed Layer 2 switch in one DIN-rail unit with eight 10/100/1000BaseT(X) ports and two SFP ports (1000/2500/10000BaseSFP). It forms an electronic security perimeter for substations, water and wastewater pumping stations, oil and gas control networks and factory PLC/SCADA systems. Deep Packet Inspection examines the data of industrial protocols including Modbus TCP, EtherNet/IP, DNP3, IEC 60870-5-104, IEC 61850 MMS, Siemens S7 Comm, OPC UA, MELSEC and Omron FINS. An intrusion prevention system is available with an additional license, and Moxa states that the series is IEC 62443-4-2 Security Level 2 certified.
Technical specifications
| Parameter |
Specification |
| Ports |
8 x 10/100/1000BaseT(X) RJ45; 2 x 1000/2500/10000BaseSFP; user-configurable DMZ ports |
| Routing performance |
Max. 350K packets per second / 2 Gbps (RFC 2544); 4K routing rules; 400K concurrent connections; 20K connections per second |
| Firewall |
Stateful router firewall and transparent (bridge) firewall; filters on IP, MAC, ports, ICMP, Ethernet protocols; DoS and DDoS protection (SYN flood, ICMP flood, ARP flood, scans) |
| IPS (license required) |
Max. 200K packets per second / 2 Gbps |
| VPN |
IPsec (max. 250 tunnels), L2TP server, OpenVPN client; AES-128/192/256, AES-256-GCM, 3DES, DES; MD5/SHA; RSA and X.509 v3; throughput up to 800 Mbps with AES-256 and SHA-256 |
| NAT / routing |
1-to-1, N-to-1, NAT loopback, port forwarding; OSPF, RIP v1/v2, static routes, VRRP; 128 VLANs |
| Redundancy |
RSTP, STP, Turbo Ring v2, Turbo Chain, VRRP |
| Security / management |
Secure Boot, RADIUS, TACACS+, 802.1X, SSH, HTTPS, SCP, SFTP, SNMPv1/v2c/v3, syslog and event log; MXsecurity management software |
| I/O / console |
Relay alarm 1 A at 24 VDC; digital input +13 to +30 V = state 1; RS-232 console (3-pin) and USB Type-C |
| Power |
12/24/48 VDC redundant dual inputs, 9.6 to 60 VDC (24 VDC DNV-certified); 0.73 A at 24 VDC; HV variants 120/240 VDC/VAC |
| Housing |
Metal, IP40, 58 x 135 x 105 mm, 1030 g; DIN rail (DNV-certified) or wall mount with kit |
| Operating temperature |
Standard -10 to 60 deg C; -T models -40 to 75 deg C; DNV-certified -25 to 70 deg C |
| Approvals as printed |
IEC 62443-4-2 Security Level 2; IEC 62368-1, UL 62368-1; EN 50121-4; NEMA TS2; ATEX, Class I Division 2; IEEE 1613, IEC 61850-3 Ed. 2.0; maritime: CCS, DNV (IEC 61162-460, IACS UR E27), KR |
| MTBF |
1,080,807 hrs (non-HV models) |
Variants
The ordering table lists the EDR-G9010-VPN-2MGSFP (12/24/48 VDC, -10 to 60 deg C) and its -T wide-temperature version, the -HV and -HV-T models for 120/240 VDC or VAC input, and the -CT and -CT-T models with PCB conformal coating. Confirm the exact code with your enquiry.
Key features for OT security projects
- All-in-one perimeter device: firewall, NAT, VPN, router and managed Layer 2 switch in one DIN-rail housing, which reduces the number of boxes in a control cabinet.
- Industrial protocol awareness: Deep Packet Inspection reads Modbus TCP, EtherNet/IP, DNP3, IEC 60870-5-104, IEC 61850 MMS, S7 Comm, OPC UA, MELSEC and FINS traffic, so rules can allow reads while blocking writes or specific function codes.
- High-speed uplinks: two SFP slots accept 1, 2.5 or 10 Gbps optics for fibre backbones between control rooms and remote stations.
- Redundant power and ring support: dual 12/24/48 VDC inputs together with Turbo Ring v2, Turbo Chain, RSTP and VRRP keep the perimeter available when a link or supply fails.
- Hardened design: metal IP40 housing, Secure Boot and wide-temperature options for outdoor kiosks and unconditioned shelters.
Where this router sits in a network
In a typical zones-and-conduits layout based on IEC 62443, the EDR-G9010 sits between the plant control network and the business or enterprise network. The PLCs, RTUs and HMIs live on protected LAN ports, an engineering workstation zone can be placed on a separate VLAN, and a user-configurable DMZ port can host a historian or data diode gateway. Only defined conduits cross the boundary: for example, an OPC UA connection from the historian to a SCADA server, or an IPsec tunnel to a remote maintenance contractor.
Because the unit also routes, it can connect several cells or pump stations that use overlapping IP schemes. One-to-one and N-to-1 NAT let machine builders deliver identical machines with identical addresses, while the plant network still reaches each one through its own translated address.
Transparent firewall mode
Where re-addressing an existing network is not possible, the transparent (bridge) firewall mode places the device inline without changing IP subnets. This is often the quickest way to add protocol filtering in front of a legacy PLC network during a short shutdown window.
Selection guidance
| Site condition |
Variant to consider |
| Air-conditioned control room, 24 VDC supply |
EDR-G9010-VPN-2MGSFP |
| Outdoor RTU kiosk or desert pumping station |
-T wide-temperature model (-40 to 75 °C) |
| Substation with 110/125 VDC or AC auxiliary supply |
-HV or -HV-T model |
| Coastal, humid or corrosive atmosphere |
-CT or -CT-T model with conformal coating |
Commissioning and maintenance
Start with a default-deny policy and add rules only for the traffic that the control system actually needs; a short period of logging before rules are enforced helps to identify legitimate flows. Change all default credentials, disable unused services and ports, and connect the unit to RADIUS or TACACS+ where central user management exists. Keep a backup of the configuration file after every approved change, and store it together with the network drawings.
Firmware should be updated under change control, ideally after testing on a spare unit. If the IPS license is used, plan how signature updates will reach a device that may have no direct internet connection, for example through MXsecurity or a managed update procedure.
Use in Oman and GCC conditions
Many oil and gas, water and power assets in the region are located in remote desert areas with high ambient temperatures inside shelters. The -T models are worth considering where cabinet temperatures can exceed the 60 °C limit of the standard model, and fibre SFP links avoid the voltage and distance limits of copper between buildings. Substation projects often ask for IEC 61850-3 and IEEE 1613 compliance, both listed for this series.
What to include in your RFQ
- Exact model code, including -T, -HV or -CT suffix.
- Number and type of SFP transceivers (1G, 2.5G or 10G; multimode or single-mode; distance).
- Whether the IPS or virtual patching license is needed, and for how many units.
- Mounting method (DIN rail or wall-mount kit) and supply voltage.
- Project end user and any required certificates or test documents.
Planning a secure OT network
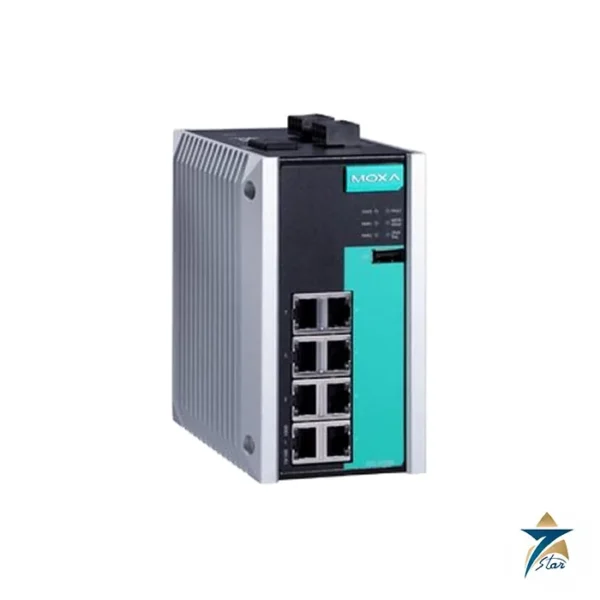
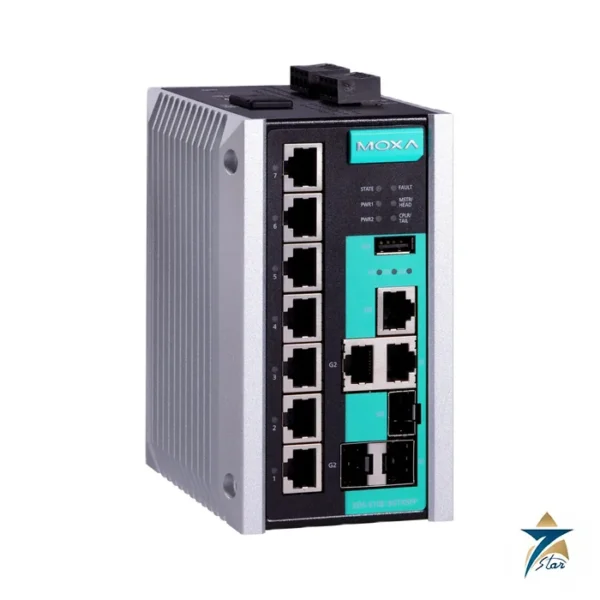
Decide the zones and conduits first: which networks sit behind the router, which protocols may cross, and who needs VPN access. Use object-based firewall rules and the four-step setup wizard for WAN, LAN and bridge ports. Virtual patching and IPS require the additional license and a management plan for signature updates. For a plain switching role, compare managed switches such as the Moxa EDS-G508E. Seven Star LLC, an independent supplier in Muscat, quotes the exact code; confirm license needs, voltage type and temperature range before ordering. The Moxa datasheet (version 3.0) is attached, and related products are in Industrial Communications. The setup wizard configures WAN, LAN and bridge ports in four steps, and object-based firewall management makes it easier to maintain IP, service and industrial-protocol rules. Firewall and VPN events can be logged locally, sent as SNMP traps or forwarded to a syslog server. Secure Boot checks system integrity, and the virtual patching feature (with the IPS license) shields known vulnerabilities in devices that cannot be patched during operation.




Reviews
There are no reviews yet.